Identity governance for Microsoft Entra ID and Active Directory
When someone joins, changes roles, or leaves your company, Adcyma creates their accounts, assigns the right access, and removes it when they go. With the audit trail to prove it.
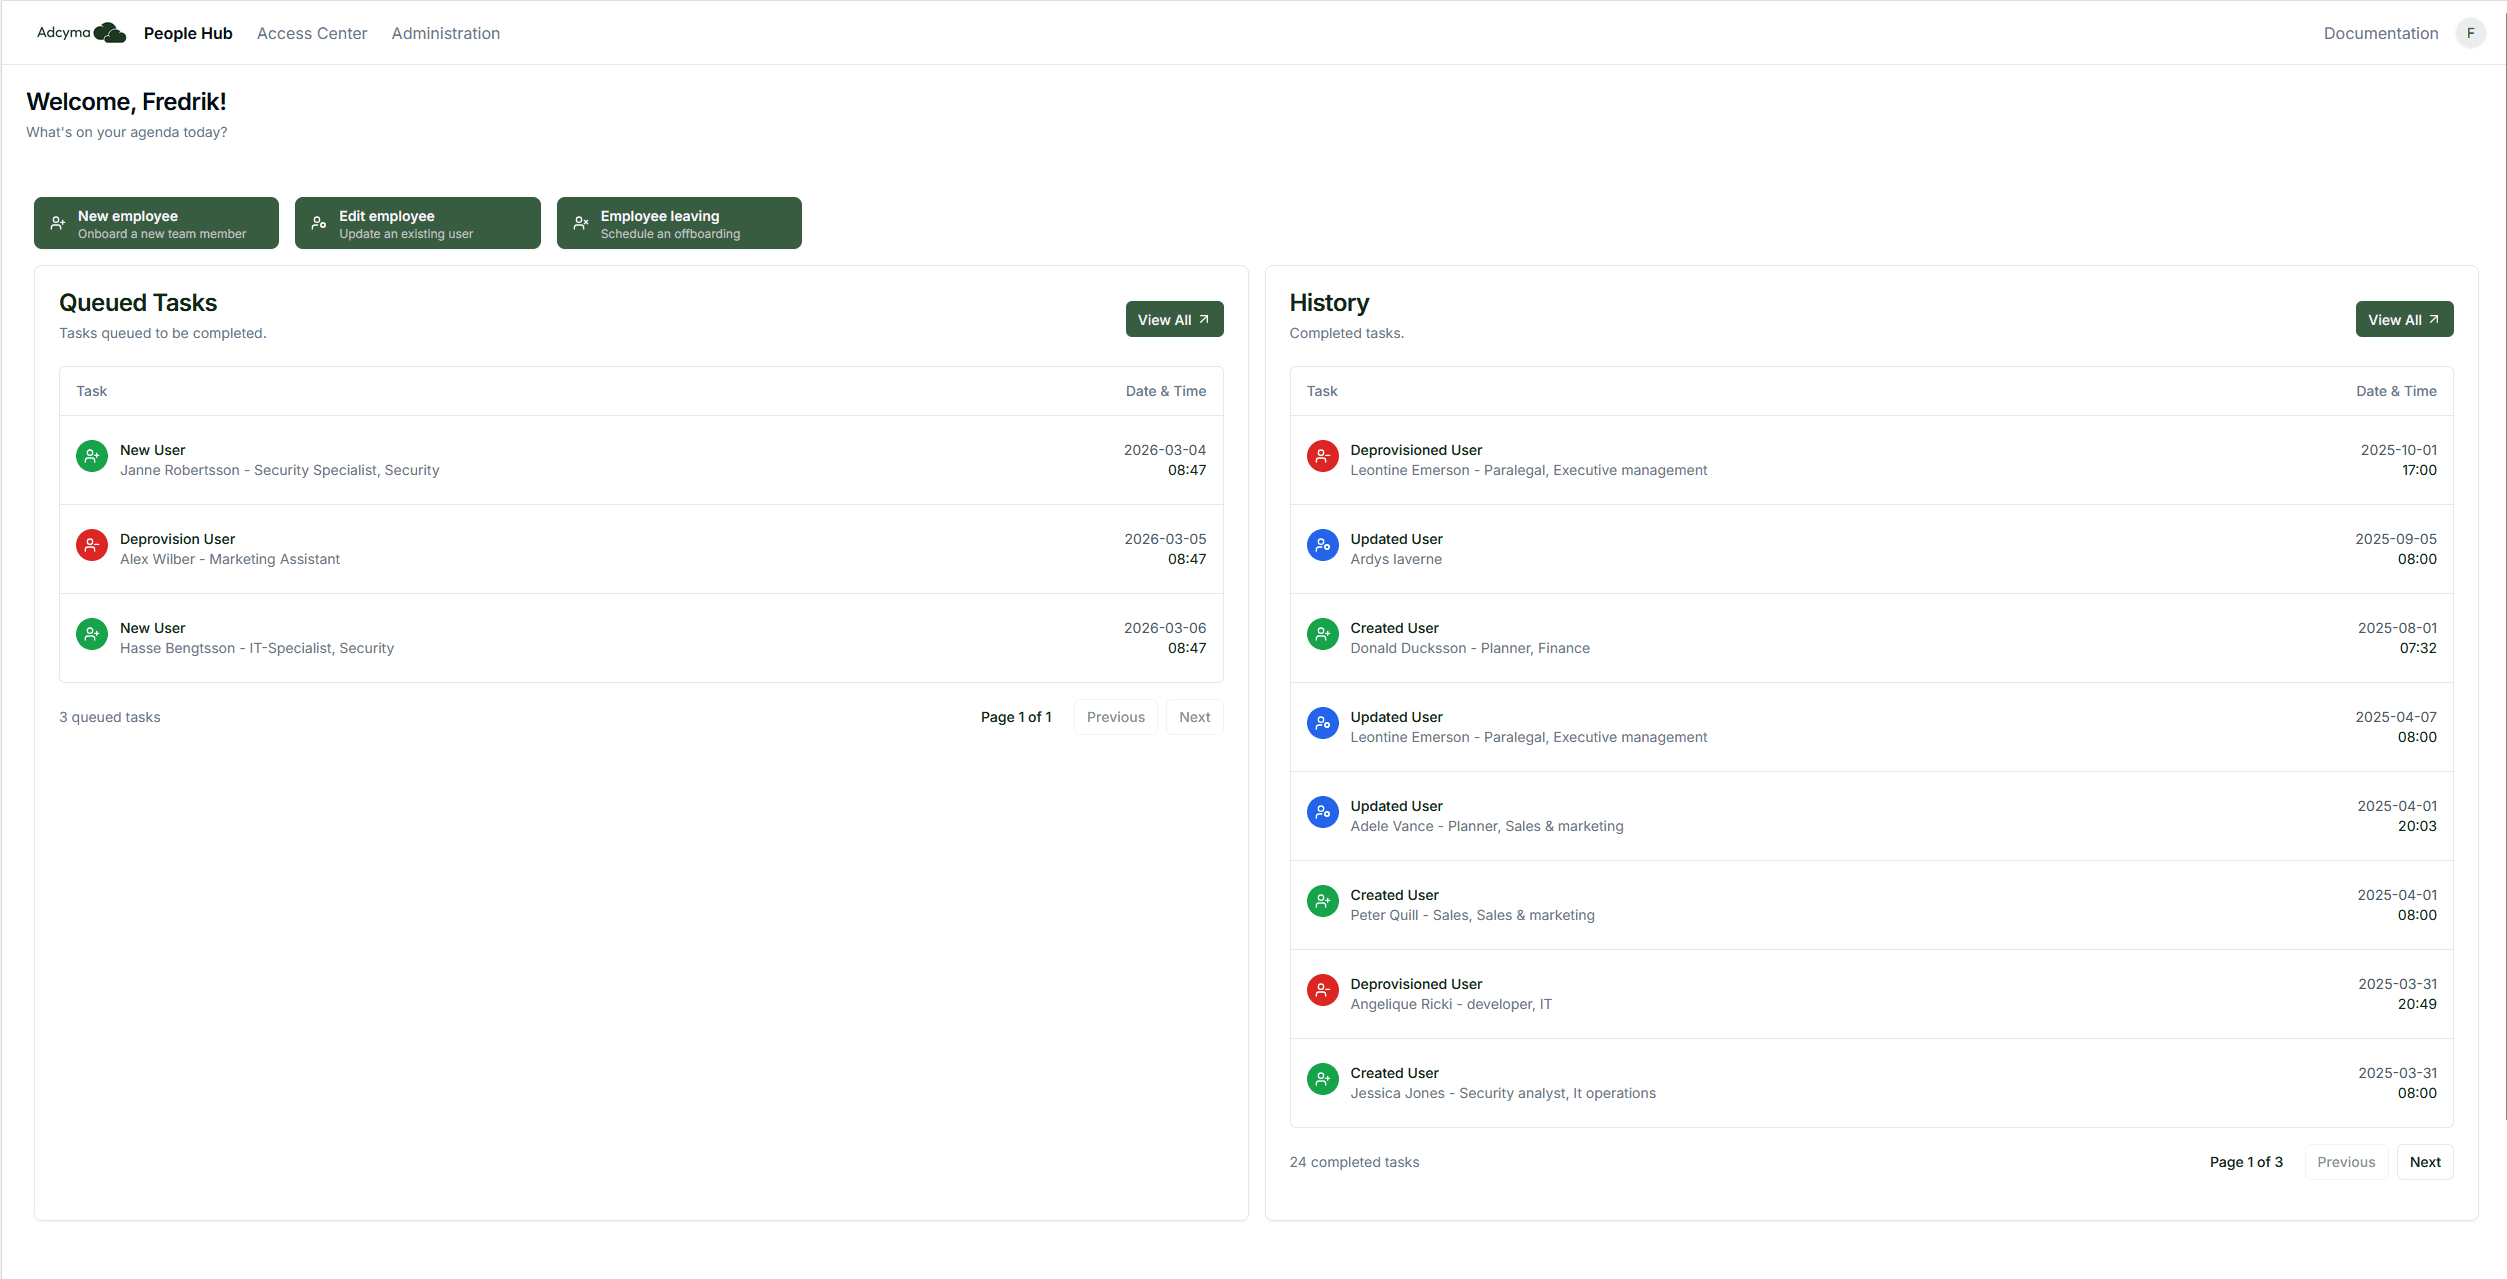
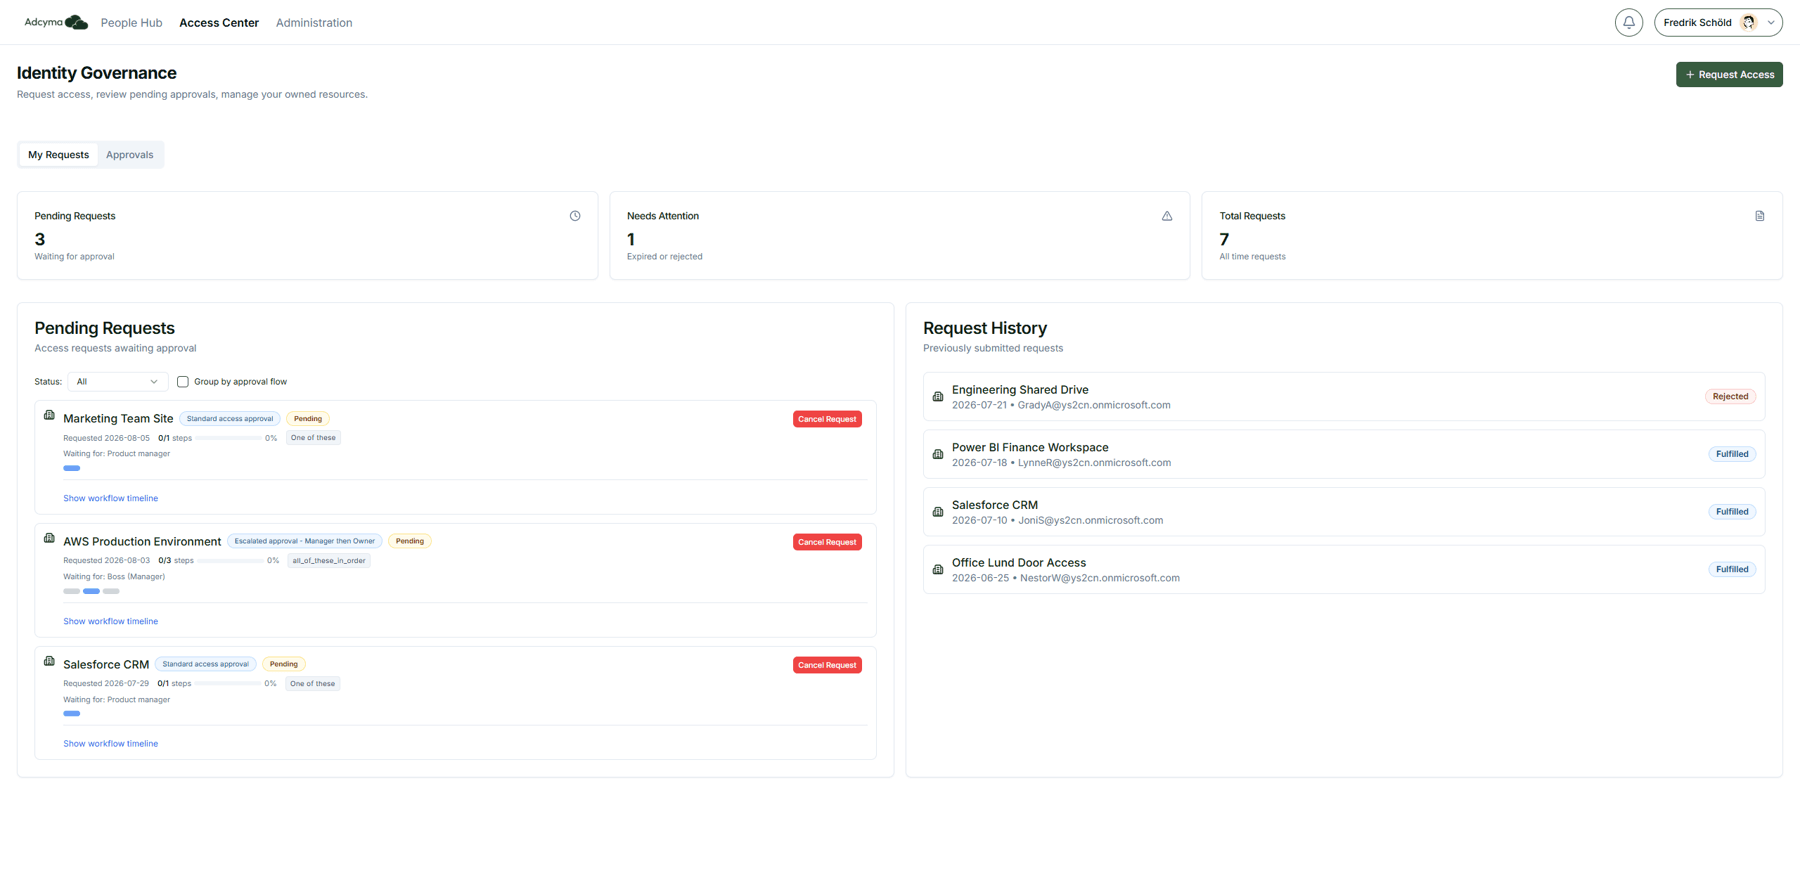
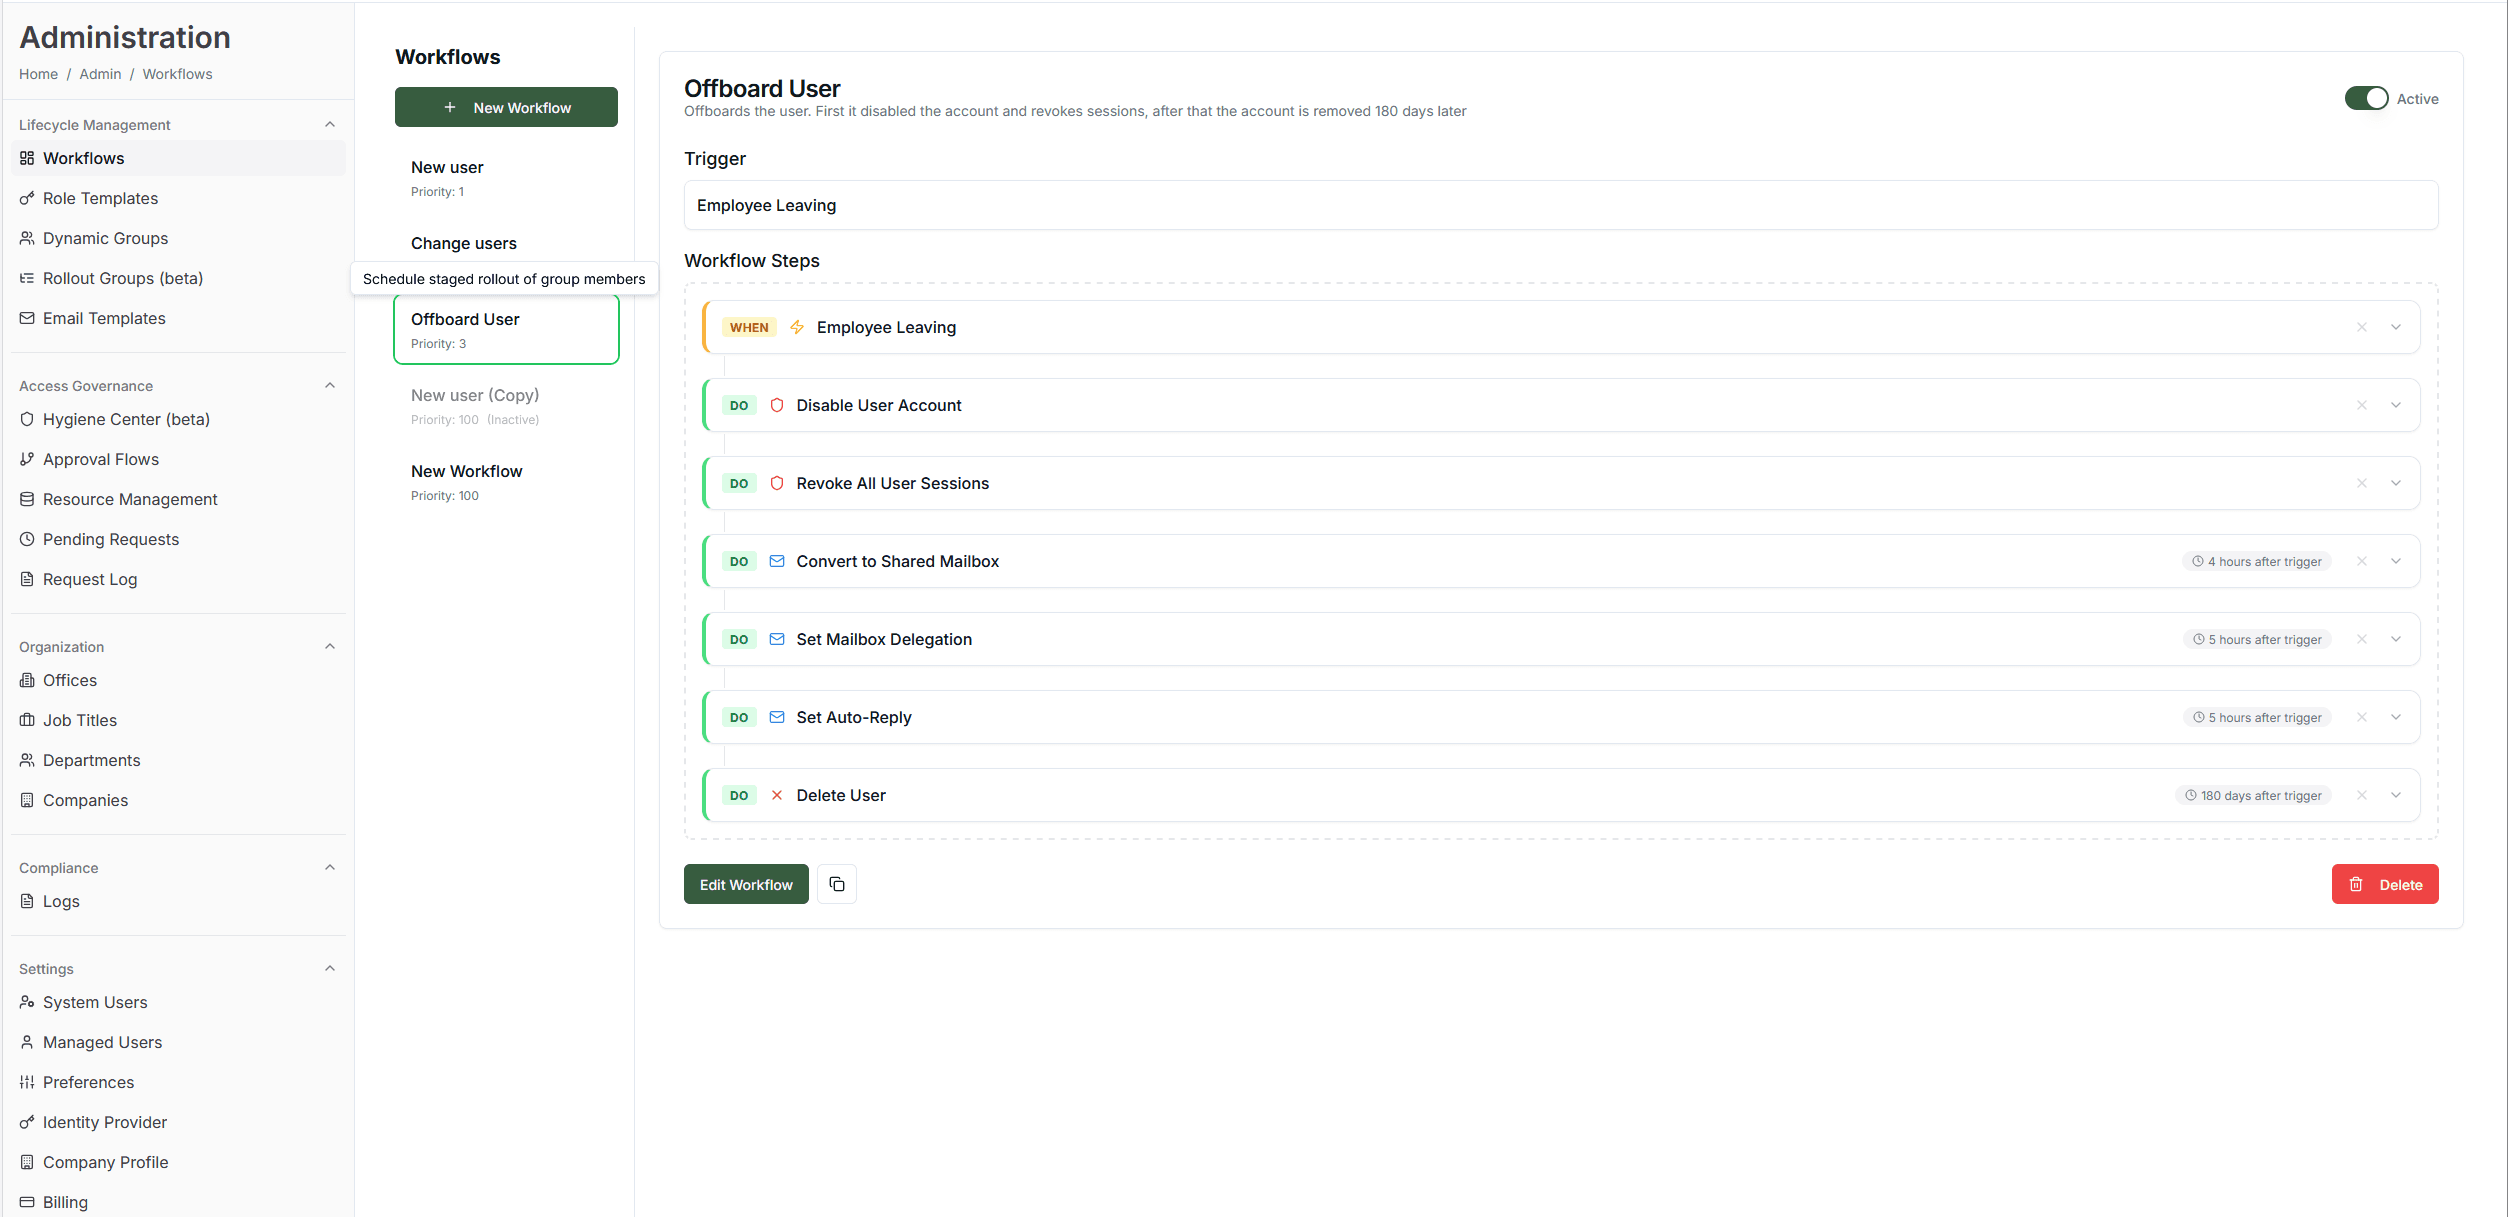
We think IGA got too complicated.
Identity governance was supposed to answer four questions.
Who is this person?
What should they have access to?
When should that access disappear?
Can we prove it happened?
Somewhere along the way, that became a six-month project. It should be boring.
Read whyWorkshops. A forty-page requirements document. Consultants who leave before the first leaver is automatically disabled.
We do not think that is necessary. IGA should be reliable, understandable, running in days. That is what we built.
What is identity governance?
Identity governance (IGA) means controlling who in your company has access to which systems, and being able to prove it. In practice: accounts are created when people start, access changes when they change jobs, everything is removed when they leave, and there is a log an auditor can read. Most companies handle this with tickets, PowerShell scripts and someone's memory. It works until that person is on holiday, or until the auditor asks. Adcyma does it automatically, across Active Directory and Microsoft Entra ID (formerly Azure AD).
Read the guide to identity governance for Entra IDAutomatic onboarding, role changes, and offboarding
Works across Active Directory and Microsoft Entra ID. Hybrid included, because hybrid is what most companies actually run.
Joiners (onboarding)
Movers (role changes)
Leavers (offboarding)
Disabled, revoked, logged. The same afternoon, not three weeks later.
Access governance
Requests, approvals, access reviews, certifications, and the evidence for all of it.
Dynamic groups
Group membership in Entra ID, Active Directory and Exchange follows rules, not tickets.
Audit evidence
An auditor should not need screenshots from five systems. When the audit comes, you export instead of reconstruct.
Let your AI agent ask, not change.
AI agents increasingly need identity data. Giving an agent Graph admin permissions to find out is a bad trade.
Adcyma's MCP server gives agents governed, read-only answers instead. Agents can ask, not change.
About Adcyma MCPFrequently asked questions
Adcyma automates the identity lifecycle in Microsoft Entra ID and Active Directory. Accounts and access are created when someone joins, updated when they change roles, and removed when they leave. It also runs access reviews and collects audit evidence.
Yes. Adcyma manages identities across on-premises Active Directory and Microsoft Entra ID, including hybrid setups where both are in use.
Days, not months. Adcyma is designed for self-service deployment by your own IT team. No consultants or implementation project required.
Those platforms were designed for a world of on-premises applications, implementation partners and year-long rollouts, and they are priced and staffed accordingly. Adcyma is built for companies running on Microsoft Entra ID and Active Directory. It covers what identity governance is actually for: onboarding, role changes, offboarding, and proving it with access reviews and audit evidence. Your own IT team deploys it in days, and you pay per user rather than per project.
From €1.50 per user per month. Free for up to 25 users. No setup fees or hidden costs.
Adcyma is built to support NIS2 access-control requirements and produces audit evidence usable for ISO 27001 controls. It does not make you compliant on its own; no tool does.
Yes, through Adcyma's read-only MCP server. Agents get governed answers about identity and access without being granted write permissions in your tenant.
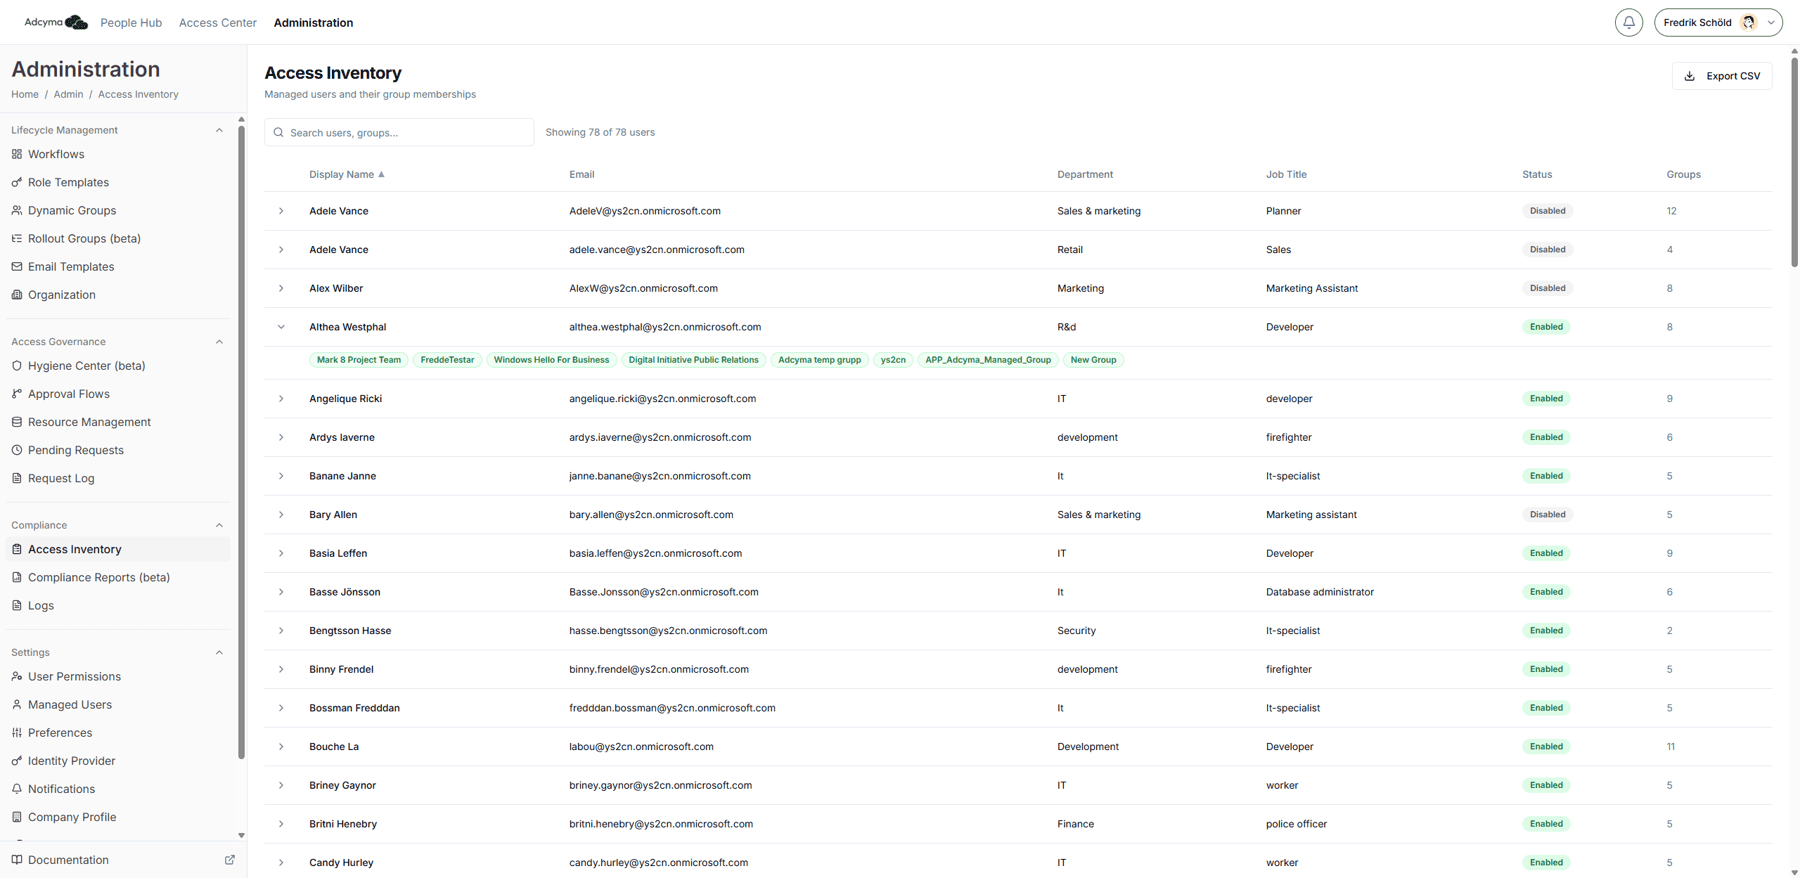
From €1.50 per user per month
Free up to 25 users. No setup fee, no credit card, no consultant, no "contact sales".
Start Free Trial- Automatic onboarding, role changes and offboarding
- Access reviews and audit evidence
- Active Directory, Entra ID and hybrid
- Live in days, not months